Swansea University Audit Uncovers Extensive GDPR Violations in British Gambling Cookie Banners
Gisela Koch · Sep 6, 2026
Swansea University Audit Uncovers Extensive GDPR Violations in British Gambling Cookie Banners
Researchers at Swansea University conducted an audit of 624 licensed British gambling websites and discovered that 86 percent of them breached GDPR rules through their cookie consent banners, and the violations often involved deceptive design techniques known as dark patterns. The study examined how these sites handled user data collection right from the initial visit, revealing patterns of pre-consent tracking for third-party marketing purposes along with banners that offered no clear rejection options on 24 percent of the platforms examined.
Details of the Audit Process and Scope
The audit focused specifically on licensed operators within the British market where strict data protection standards apply under GDPR legislation, and researchers analyzed each site's consent mechanisms to check compliance levels against established legal requirements. Data collection occurred without explicit user approval in many cases, while automatically selected invasive settings further complicated the process for visitors attempting to maintain control over their personal information. Observers note that such practices directly contradict the principles of informed consent that form the foundation of European data privacy regulations.
Major Operators Identified in the Findings
Among the sites flagged in the results were well-known names including Ladbrokes, William Hill, Hollywood Bets, Admiral Casino, and Dafabet, each of which demonstrated issues with their cookie consent implementations according to the Swansea University analysis. These operators represent a cross-section of the industry yet all appeared in the group showing violations, highlighting how widespread the problem extends even among established players in the sector. The patterns observed included banners that collected data before users could respond and defaults set to allow broad sharing with third parties without affirmative action from the visitor.
Comparison With Broader Compliance Claims
These results stand in contrast to statements from the Information Commissioner's Office, which has claimed 95 percent compliance rates among the UK's top 1,000 websites overall. The gambling sector audit suggests that specialized industries may face different challenges or apply different approaches to consent mechanisms compared to general web properties tracked in broader surveys. Researchers compared their specific findings against these general benchmarks to underscore the gap between reported averages and actual performance within this regulated market segment.
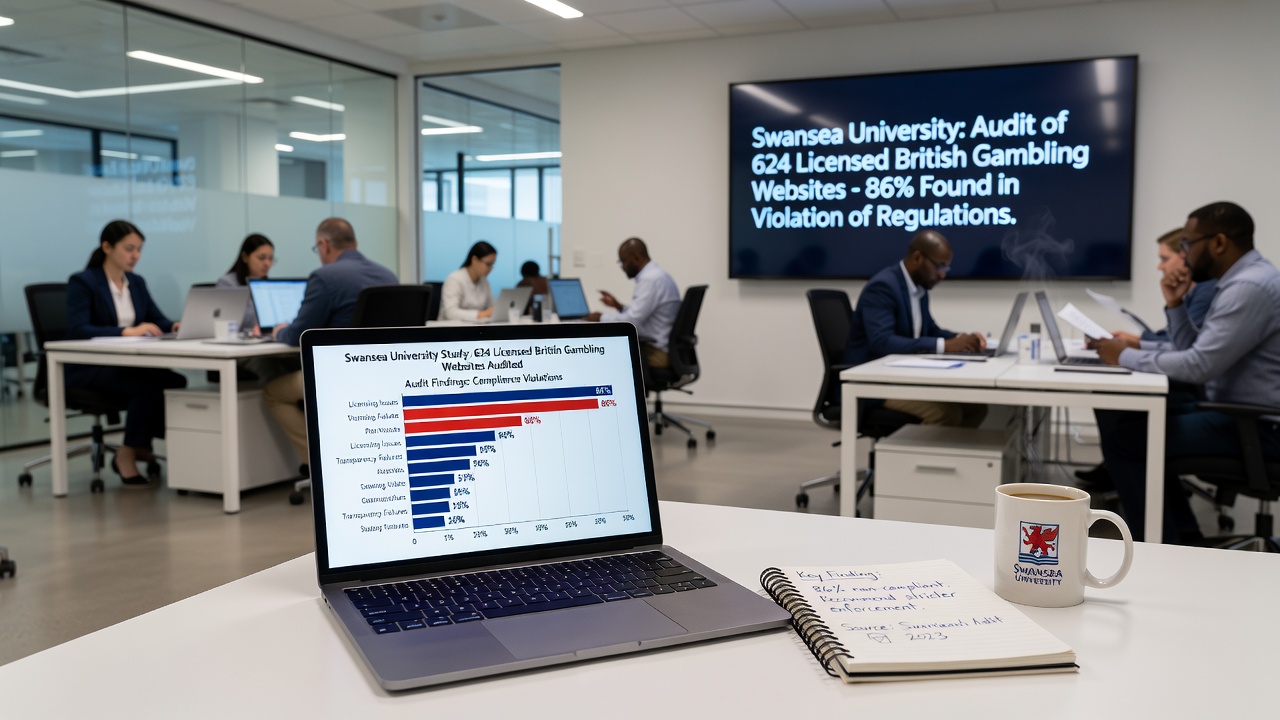
Further examination showed that 24 percent of the audited sites provided no rejection option at all within their banners, forcing users either to accept terms or navigate away entirely. This absence of choice represents one of the clearer examples of non-compliance identified during the review process. Additional dark patterns included pre-ticked boxes that enabled extensive data sharing and interfaces designed to guide users toward approval rather than presenting balanced options for control over their information.
Technical Aspects of the Violations Observed
GDPR requires that consent must be freely given, specific, informed, and unambiguous, yet the banners reviewed frequently fell short on multiple criteria simultaneously. Pre-consent data collection for third-party marketing directly violates the requirement that processing begin only after valid permission has been obtained. Sites that defaulted to invasive settings placed the burden on users to actively opt out rather than starting from a neutral position, another point of departure from regulatory expectations. Those who've studied consent interface design recognize these elements as common tactics that reduce user agency while still appearing functional at first glance.
Context Within UK Data Protection Landscape
British gambling websites operate under dual oversight from both gambling regulators and data protection authorities, which creates layered compliance expectations that extend beyond standard website practices. The audit results indicate that meeting these combined standards requires more precise implementation of consent tools than many operators have currently achieved. Data from the study provides concrete examples of where gaps exist between legal requirements and day-to-day website behavior across hundreds of platforms.
What's interesting about the findings is how consistently the violations appeared across different types of gambling sites rather than clustering among smaller or less established operators. This distribution suggests systemic issues in how the industry approaches cookie management rather than isolated incidents limited to particular companies. The 86 percent violation rate emerges from a sample size large enough to reflect broader trends within the licensed British market, giving weight to the patterns documented by the Swansea University team.
Conclusion
The Swansea University audit of 624 licensed British gambling websites delivers measurable evidence of GDPR non-compliance through cookie consent banner practices, with 86 percent showing violations that include pre-consent data collection, missing rejection options, and default invasive settings. Major operators such as Ladbrokes, William Hill, Hollywood Bets, Admiral Casino, and Dafabet appeared among those identified, while the results differ from the Information Commissioner's Office general compliance figures for top UK websites. These documented patterns provide specific data points for ongoing discussions around data privacy implementation in regulated online sectors. Audit of 624 UK gambling sites on cookie consent and GDPR compliance (Swansea University study) offers further detail on the methodology and specific metrics collected during the review.